Solutions

Autonomous Pentesting

You develop with autonomous tools. You still pentest with humans.
That's not a fair fight. Sybil runs autonomous penetration testing engagements — black box or white box, your call — with the same kind of intelligence, at the same pace, that's already shipping your code. Every finding is independently reproduced before you ever see it, ships with a CWE ID, a CVSS score, and remediation precise enough to hand an autonomous coding assistant, with retesting available once the fix lands.
Trusted by security & engineering teams — including at Carta
Notion logoCursor logoThinking Machines logoCarta logoBaseten logo
10
x
the rate AI coding agents can already out-produce human code review. That's the pace validation now has to match.
(Forrester, Agentic Development Security, 2026)
60%
of organizations Gartner expects to adopt structured exposure validation by 2029.
(Gartner Market Guide for Adversarial Exposure Validation)
~2:1000
AppSec engineers per developer at the median enterprise, and that's before we consider how agentic development is scaling their output.
(Industry AppSec hiring benchmark, 2026)
71
%
of AppSec job postings call for scanning tool skills. Only 24% call for remediation.
(Industry AppSec hiring benchmark, 2026)
It runs the engagement, not a checklist.
Every Sybil engagement moves through the same pipeline, whether it's a one-time pentest or ongoing coverage — access confirmed, surface mapped, techniques chained, findings independently reproduced, fixes shipped back.
01
Access & recon
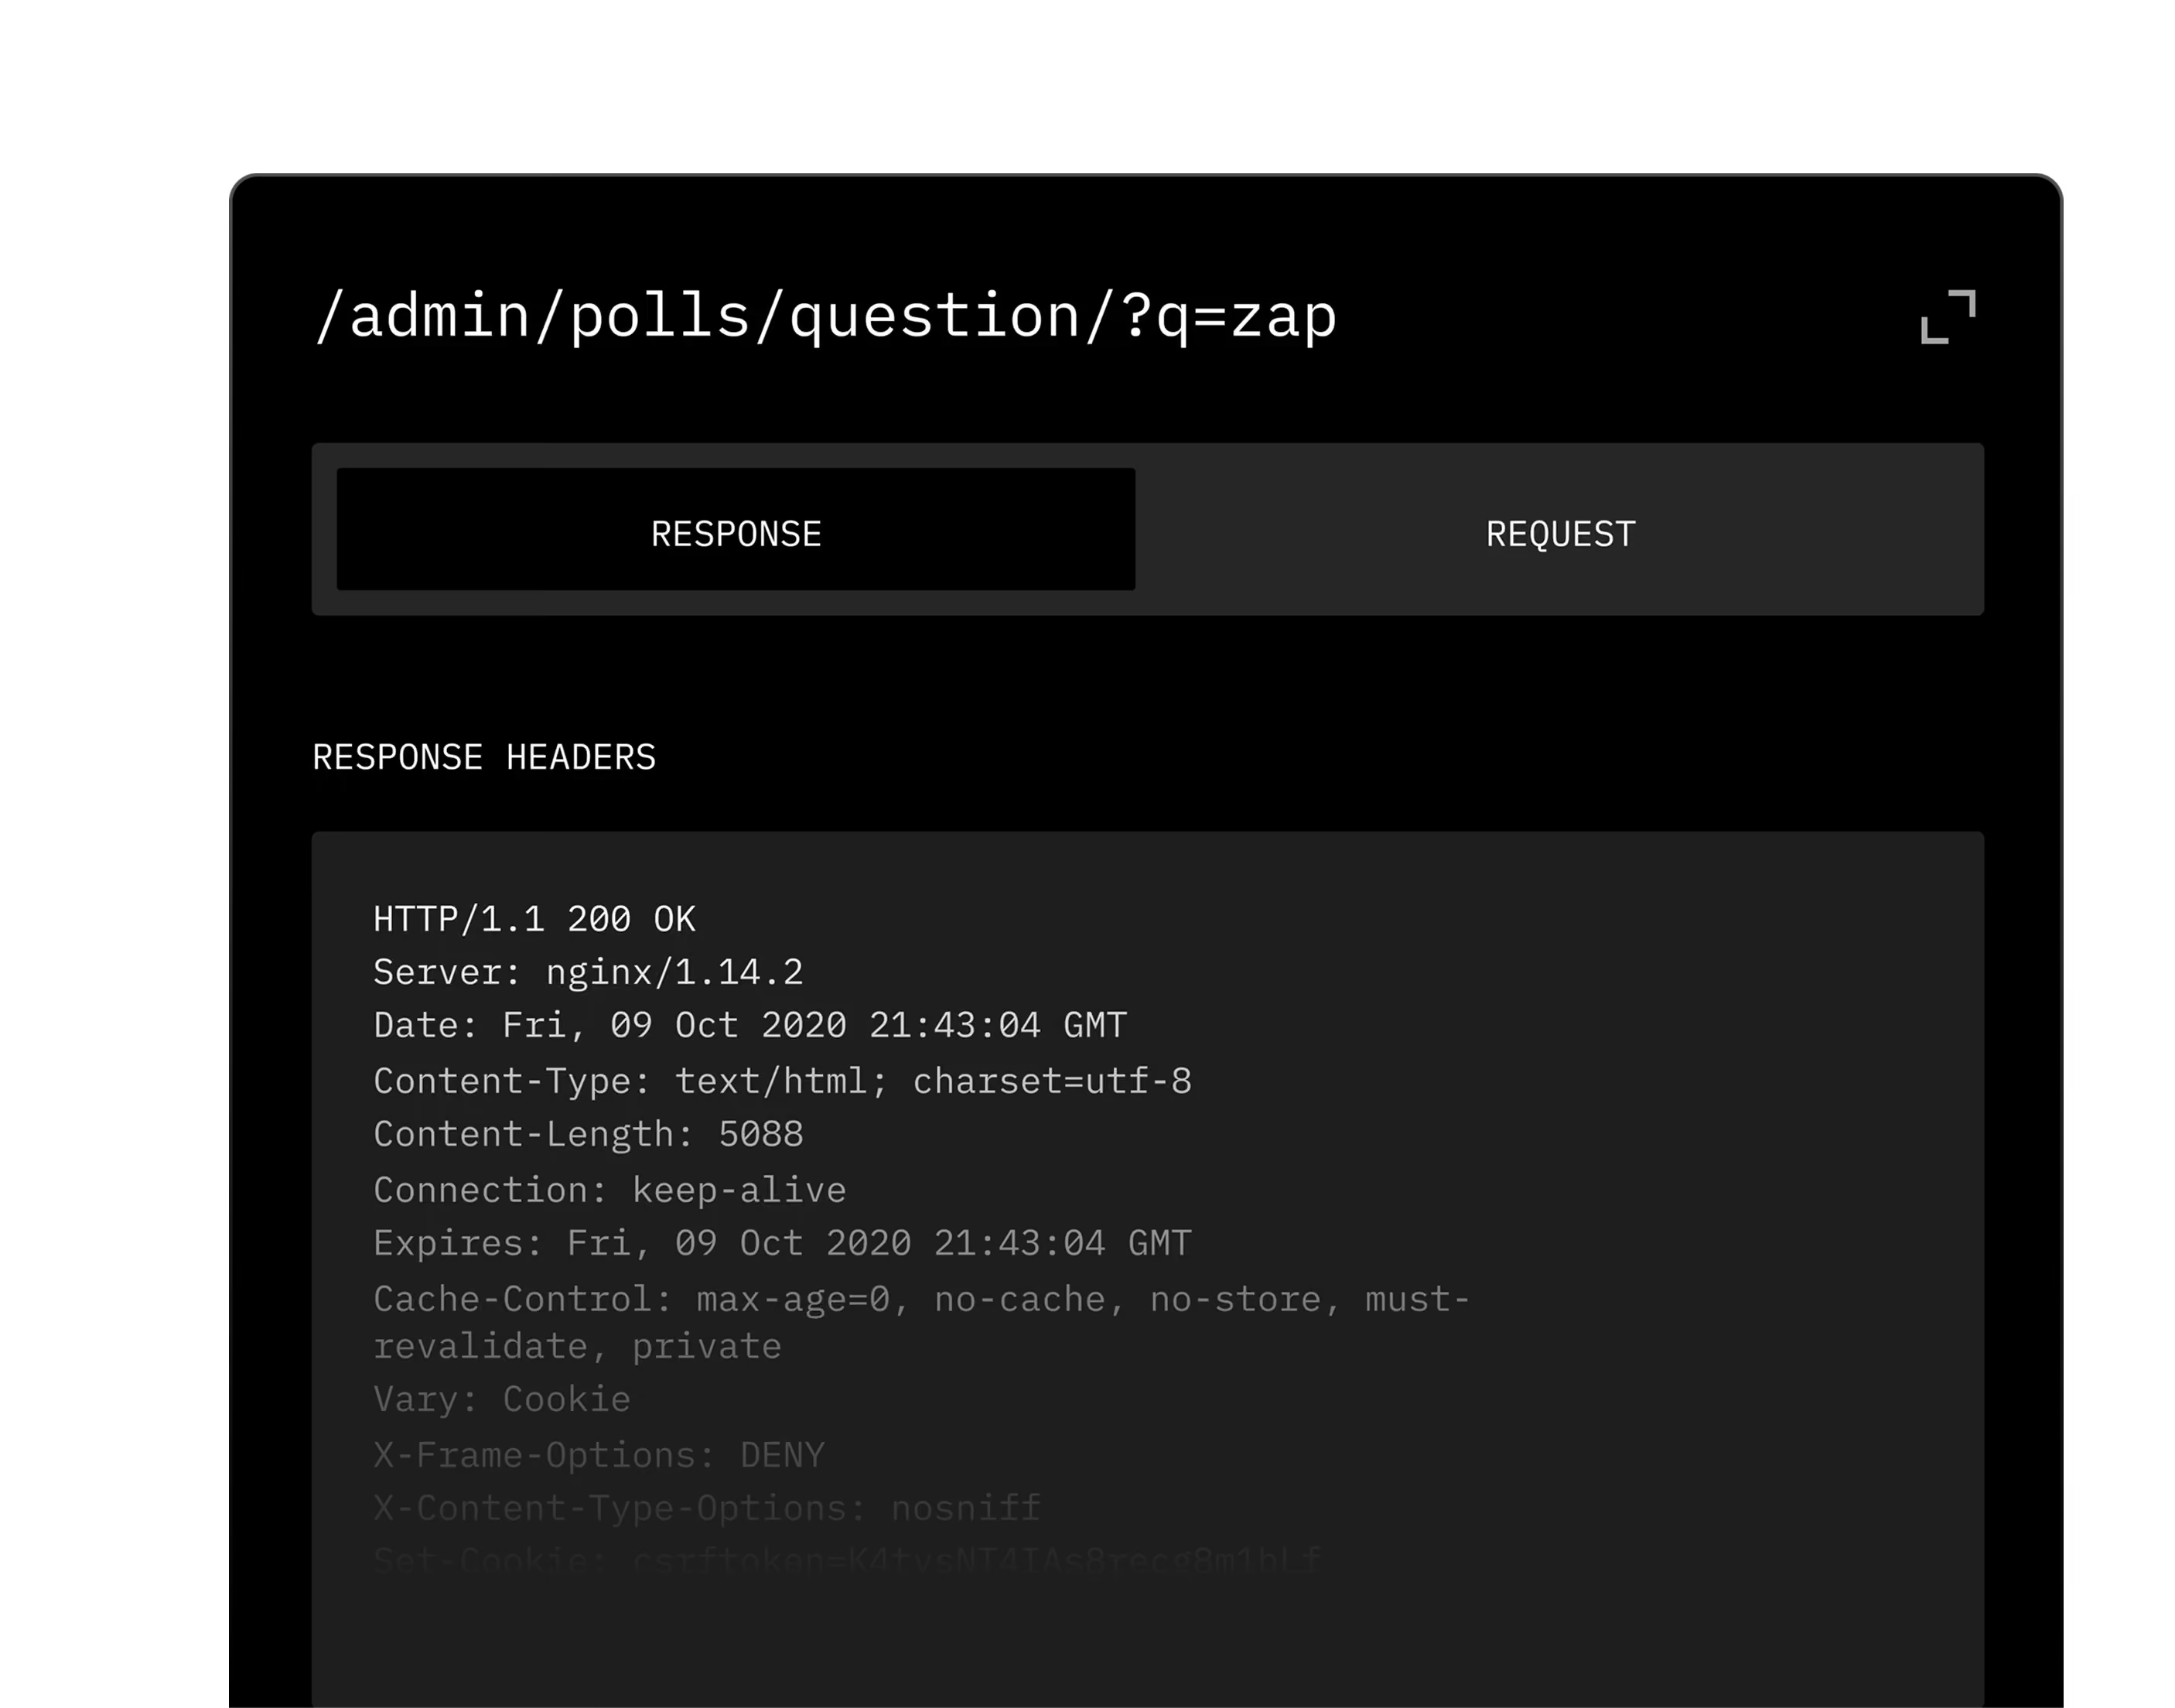
Credentials and scope are confirmed, then every reachable endpoint, page, and API inside that scope gets mapped.
Screenshot showing a web server response with HTTP 200 OK status and related headers in a black interface.
/admin/polls/question/?q=zap
Expand icon
Response
Request
Response headers
HTTP/1.1 200 OK Server: nginx/1.14.2 Date: Fri, 09 Oct 2020 21:43:04 GMT Content-Type: text/html; charset=utf-8 Content-Length: 5088 Connection: keep-alive Expires: Fri, 09 Oct 2020 21:43:04 GMT Cache-Control: max-age=0, no-cache, no-store, must-revalidate, private Vary: Cookie X-Frame-Options: DENY X-Content-Type-Options: nosniff Set-Cookie: csrftoken=K4tvsNT4IAs8recg8m1bLf

02

Plan & execute

Testing is prioritized by risk, then real attack techniques get run against the target — not a fixed checklist.
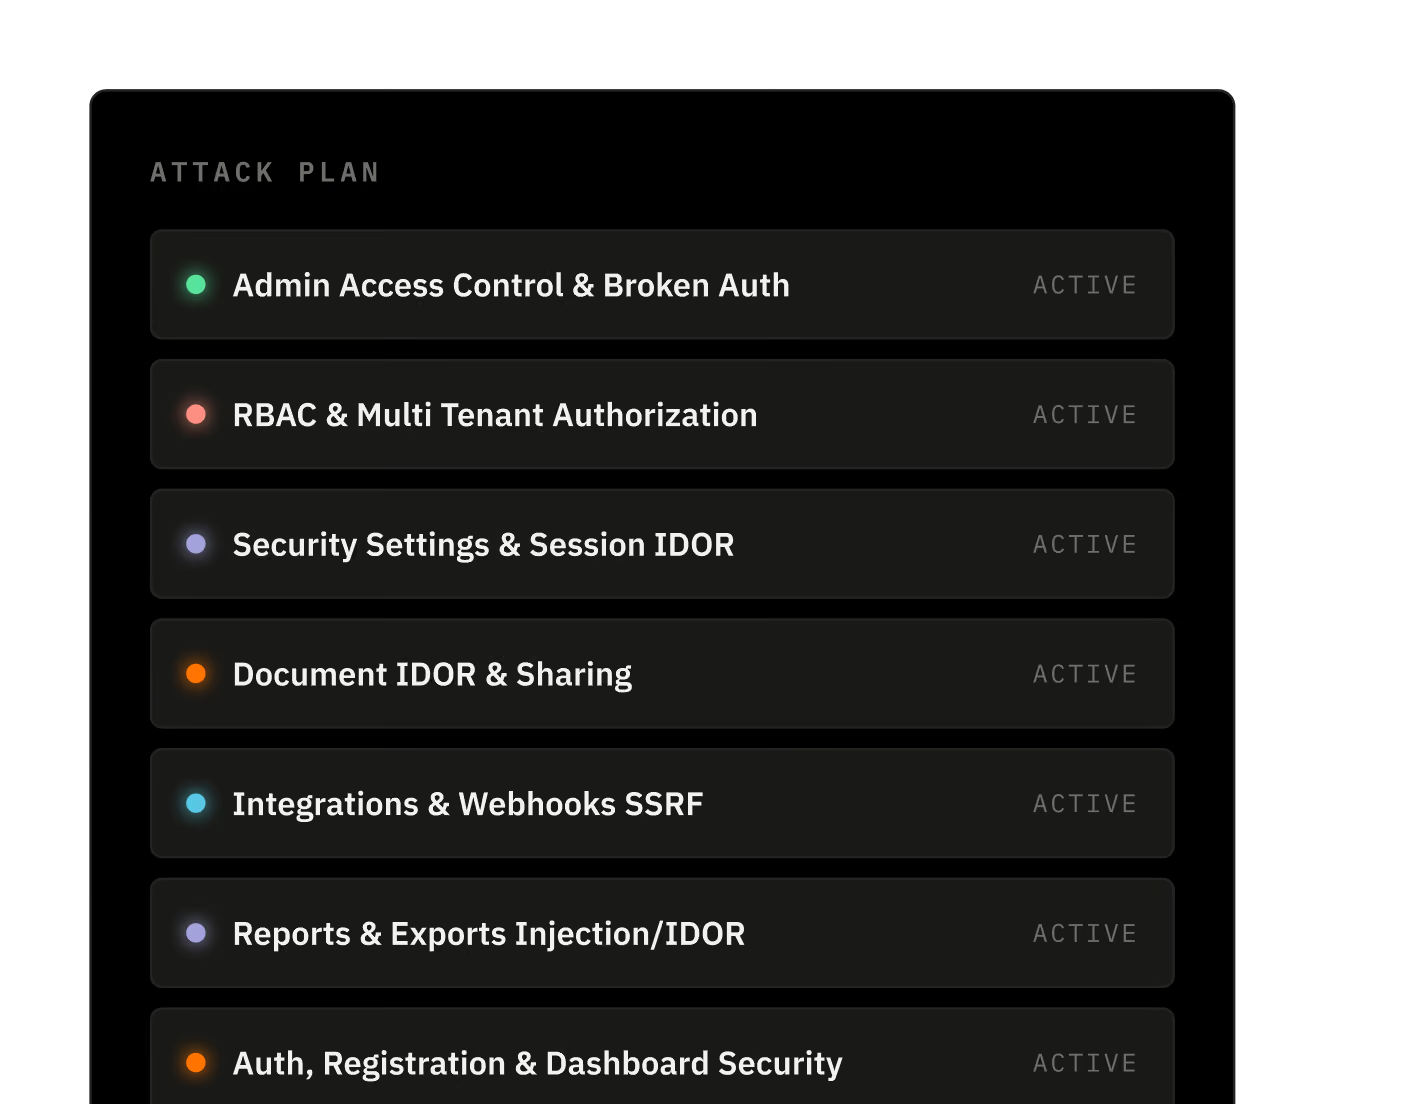
Attack Plan list showing categories like Admin Access Control & Broken Auth, RBAC & Multi Tenant Authorization, all marked Active.

03

Identify

Anything that looks like a real weakness gets flagged as a candidate finding.
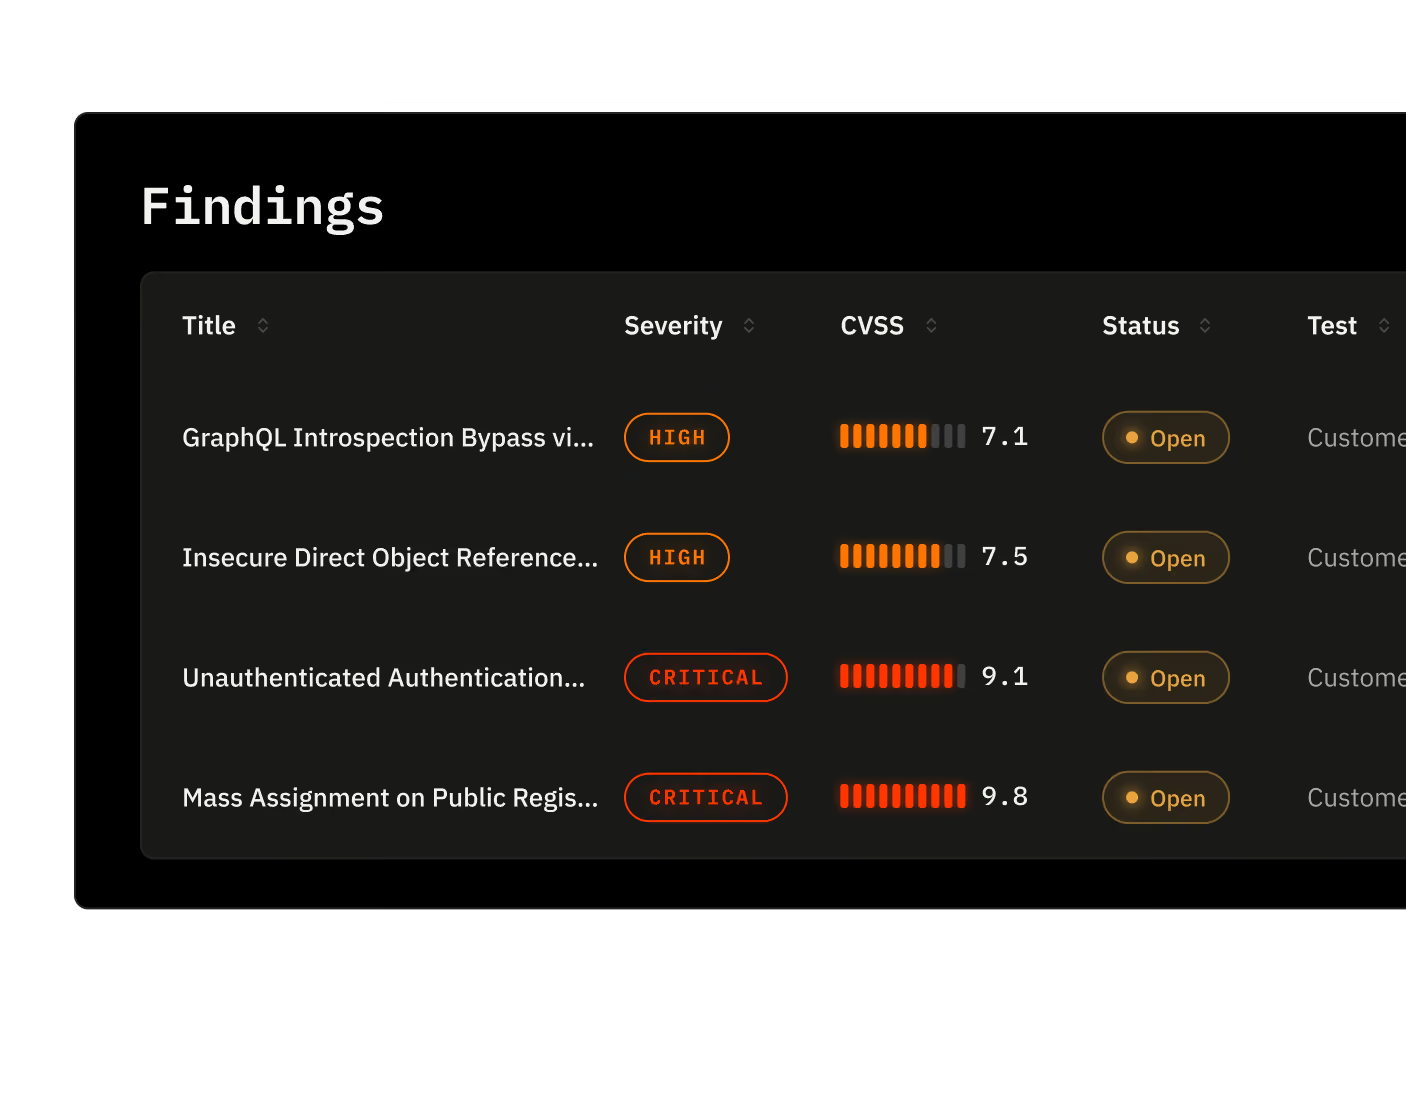
Findings table listing vulnerabilities with severity, CVSS score, status, and test type.

04

Validate & escalate

A separate pass independently reproduces it into a canonical finding, then chains it to see how far a real attacker could actually get.
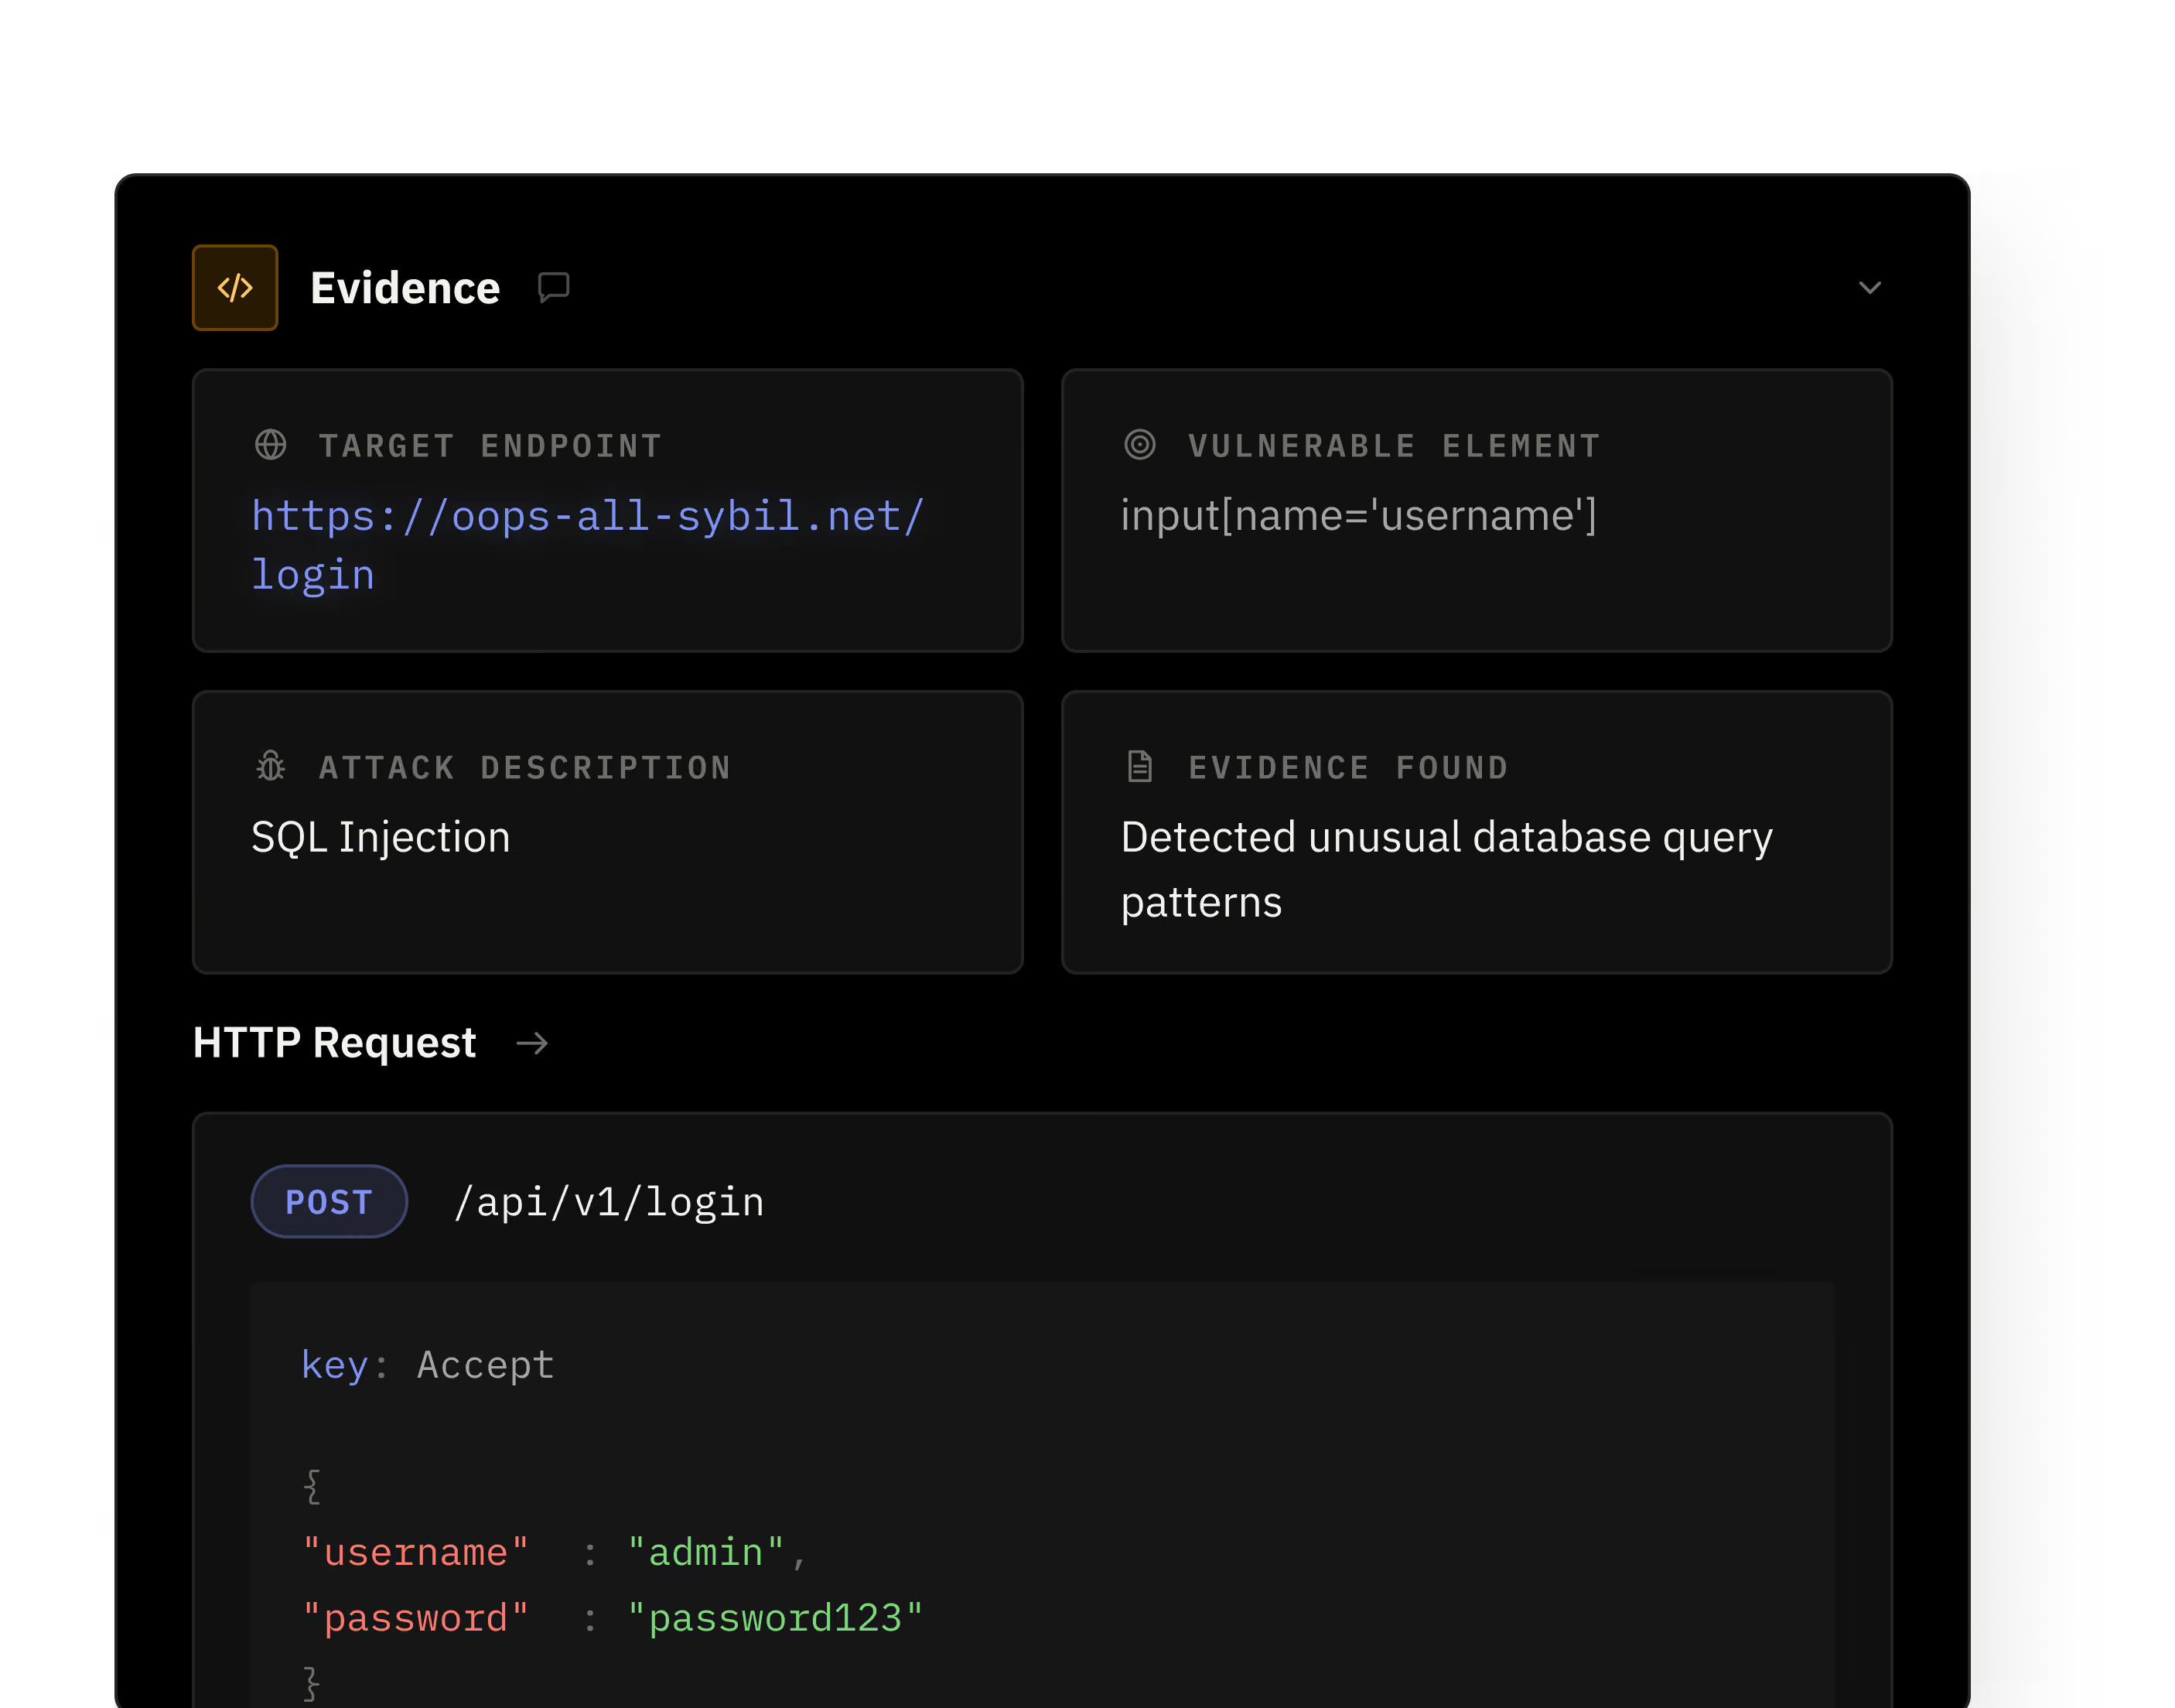
Security report showing SQL injection attack evidence on login endpoint with unusual database query patterns.

/api/v1/findings/4471/validate

Expand icon

Response

Request

Response headers

HTTP/1.1 200 OK Server: nginx/1.14.2 Date: Fri, 09 Oct 2020 21:52:03 GMT Content-Type: application/json Content-Length: 866 X-Finding-Status: confirmed X-False-Positive: false Cache-Control: no-store

05

Remediate & retest

Fix guidance ships precise enough to hand an autonomous coding assistant, with retesting available to confirm it holds.
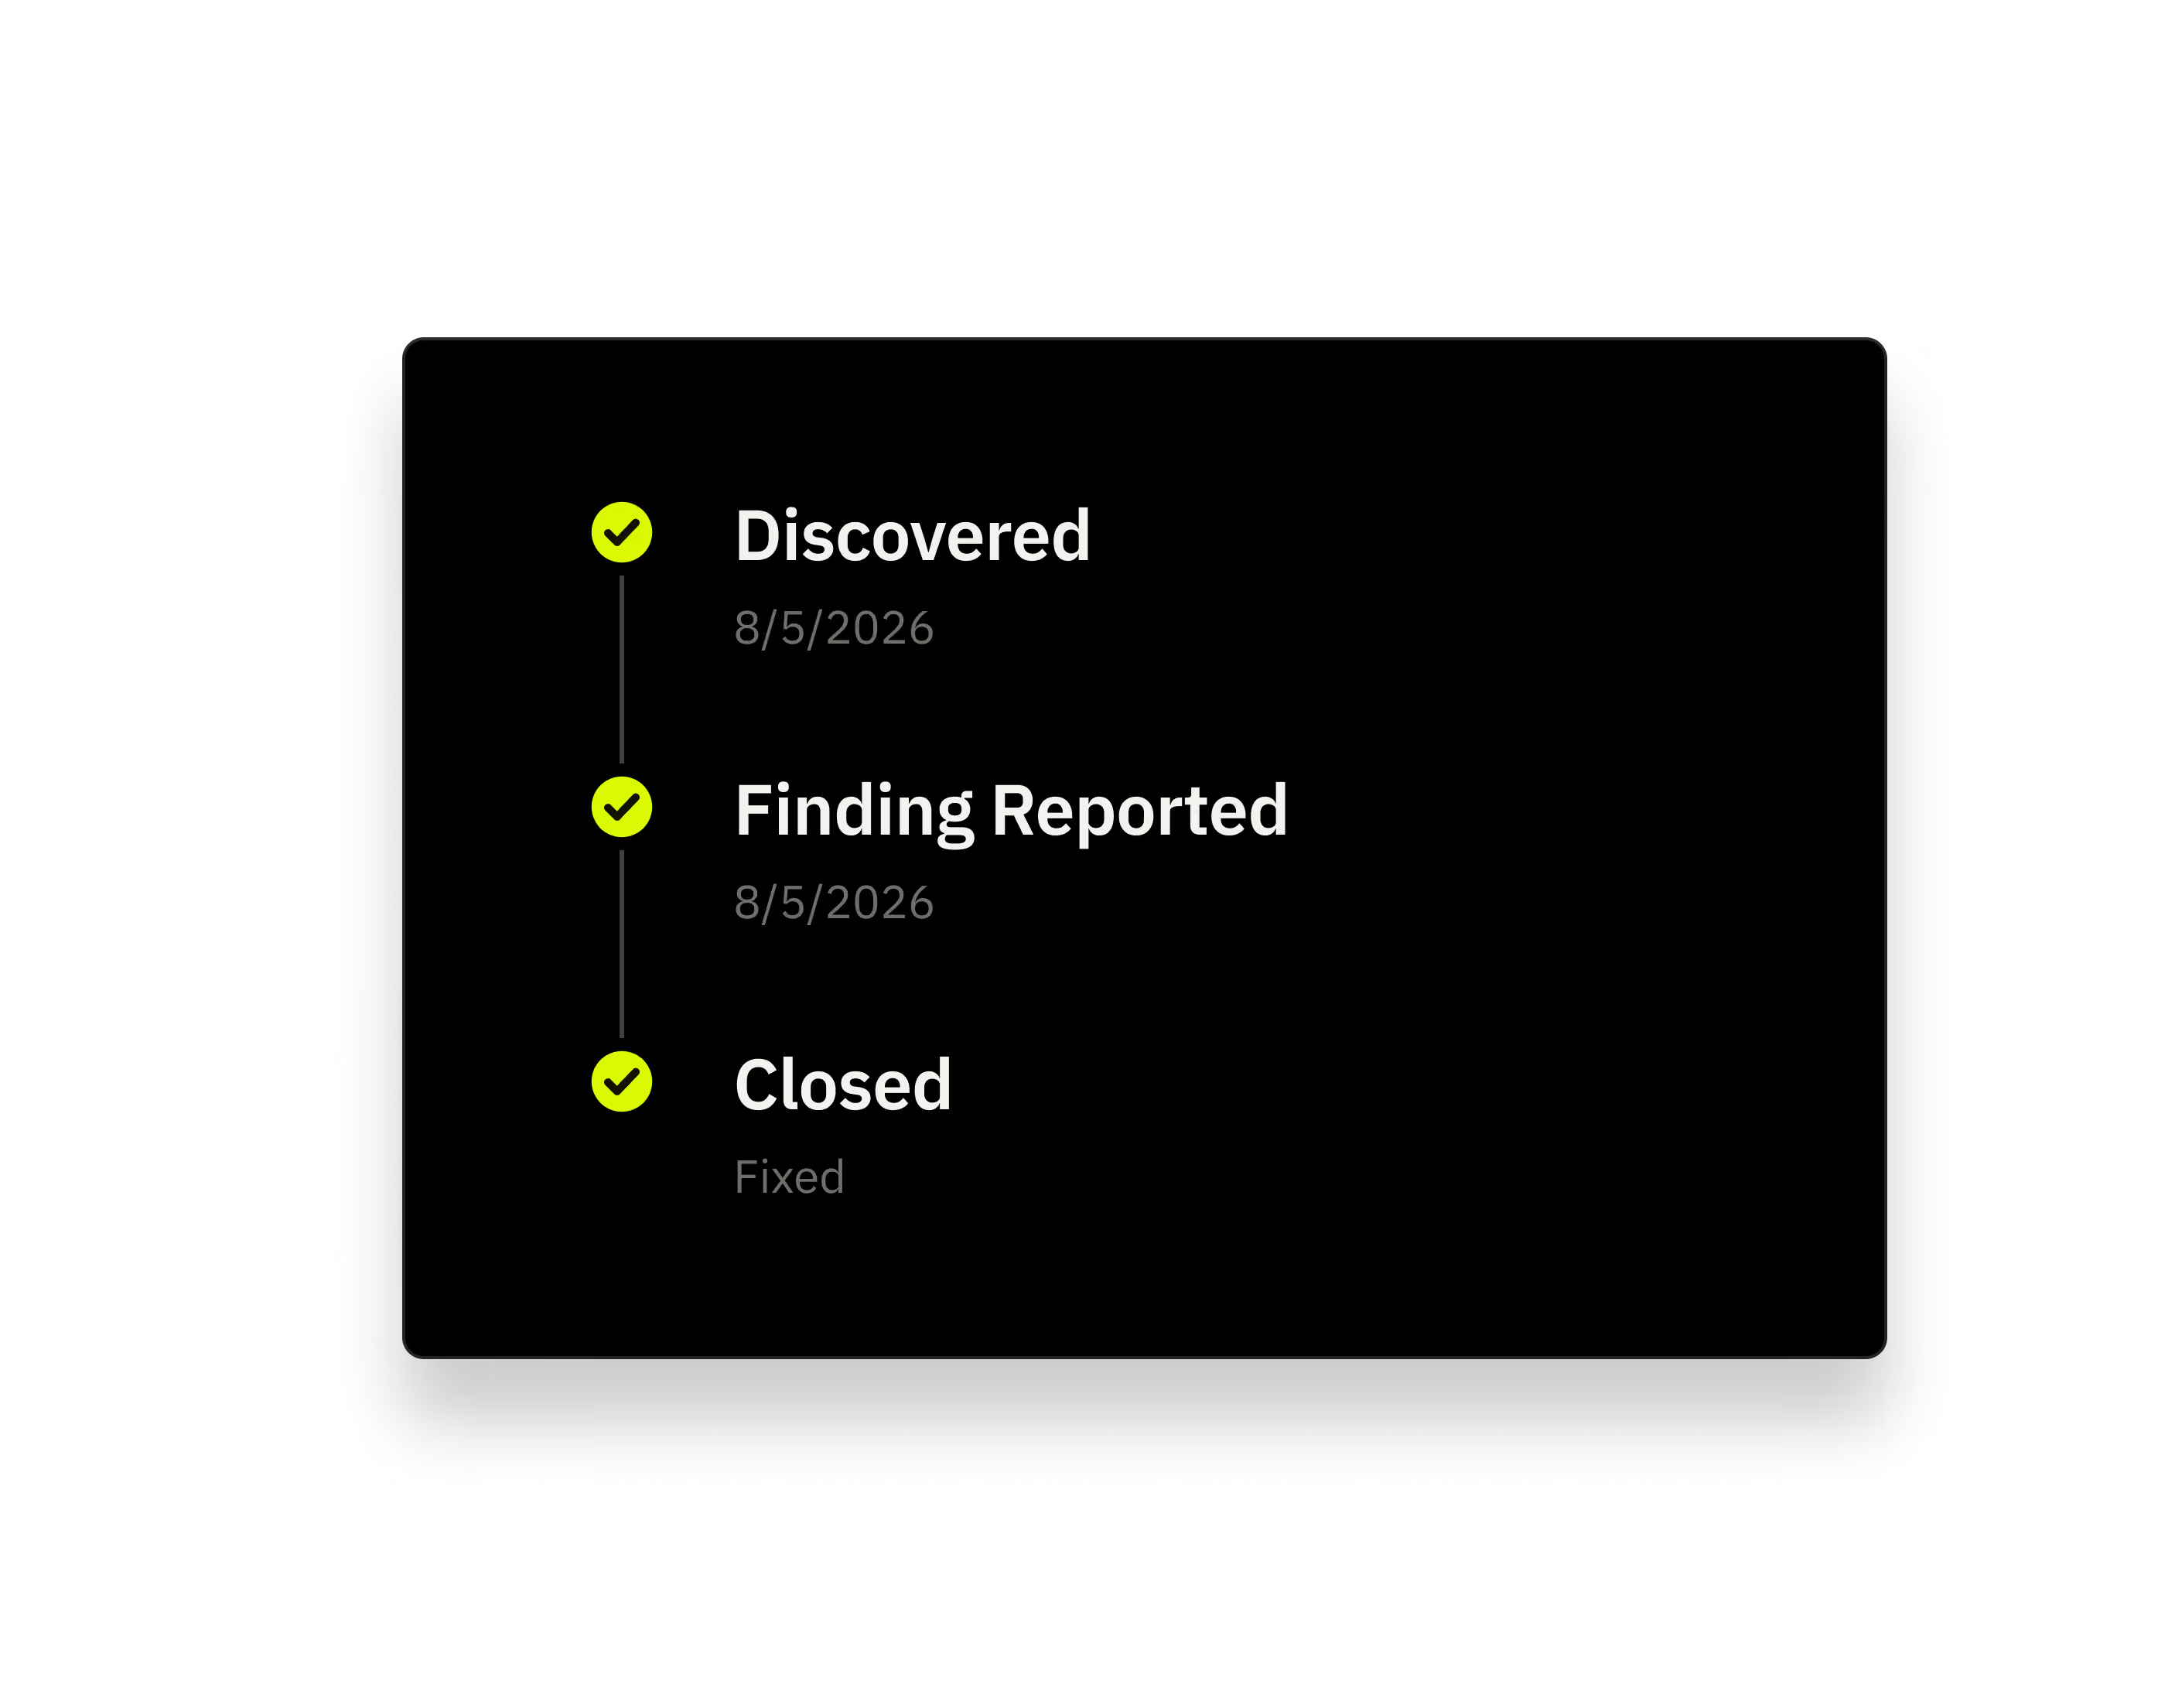
Timeline showing three completed steps: Discovered, Finding Reported on 8/5/2026, and Closed (Fixed).

/api/v1/findings/4471/remediate

Expand icon

Response

Request

Response headers

HTTP/1.1 200 OK Server: nginx/1.14.2 Date: Fri, 09 Oct 2020 22:03:41 GMT Content-Type: application/json Content-Length: 512 X-Remediation-Status: patched X-Retest-Result: pass Connection: keep-alive

What this is built on
Four commitments, and one we think the industry should adopt.
1
Validation velocity matches development velocity
Engineering output is compounding, increasingly agent-authored. Security validation has to compound with it too: continuous re-testing as code and attack surface change, not an annual engagement.
Industry velocity roughly doubled year over year, 2026
2
Continuous understanding of the attack surface
Know what exists, what changed, and where exposure moved. Most teams are flying without this today.
Only 30% of teams are confident in 90%+ visibility
3
Test and validate, not just scan
Sybil exercises the application and proves exploitability, rather than adding to a queue of theoretical findings someone else has to triage.
Gartner’s own definition of Adversarial Exposure Validation
4
Findings close the loop into engineering
Validation and remediation land inside the sprint, the PR, the pipeline, not a side queue that depends on someone chasing it down.
Detection tooling still outpaces remediation tooling roughly 3 to 1
5
The one we think should be industry standard
Coverage becomes a heat map, not a snapshot
Every validated result updates a live picture of where exposure concentrates and where it’s proven clean, so the next round of testing knows where to look first. That same picture doubles as the defensible record for your board, your auditors, and your next funding round’s security review. We think that’s what “coverage” should mean industry-wide, not an asset count.
Also satisfies the requirement for
The report your auditor, customer, or insurer needs.
Checkmark icon
SOC 2 Type II
Checkmark icon
Pre-release / annual pentest requirement
Checkmark icon
Customer security questionnaires
Checkmark icon
Cyber insurance renewal
AICPA SOC 2 certification badge
SOC 2 Type II
Sybil itself runs under SOC 2 Type II — independently audited over time, not assessed once.
Shield with padlock icon representing per-customer data isolation
Per-customer isolation
Scope, findings, and credentials are segmented per customer. Nothing crosses organization boundaries.
Amazon Web Services (AWS) logo
Hosted on AWS
Data encrypted both in flight and at rest.
Is this you
Built for teams who need a real test, on their timeline.
AI-authored code, and growing
Outnumbered by engineers and agents
Existing AppSec budget & battle scars
Leader ready to design-partner the metrics
Small security team, big engineering org
Let’s look at what changed in your last 100 PRs.

Bring us the app. We'll tell you honestly whether black box, white box, or both is the right way to test it — then run it in days, not quarters.