

SOC 2 Penetration Testing
Sybil runs SOC 2 pentesting for teams like Notion and Cursor. Cursor's engagement ran start to finish in two weeks.
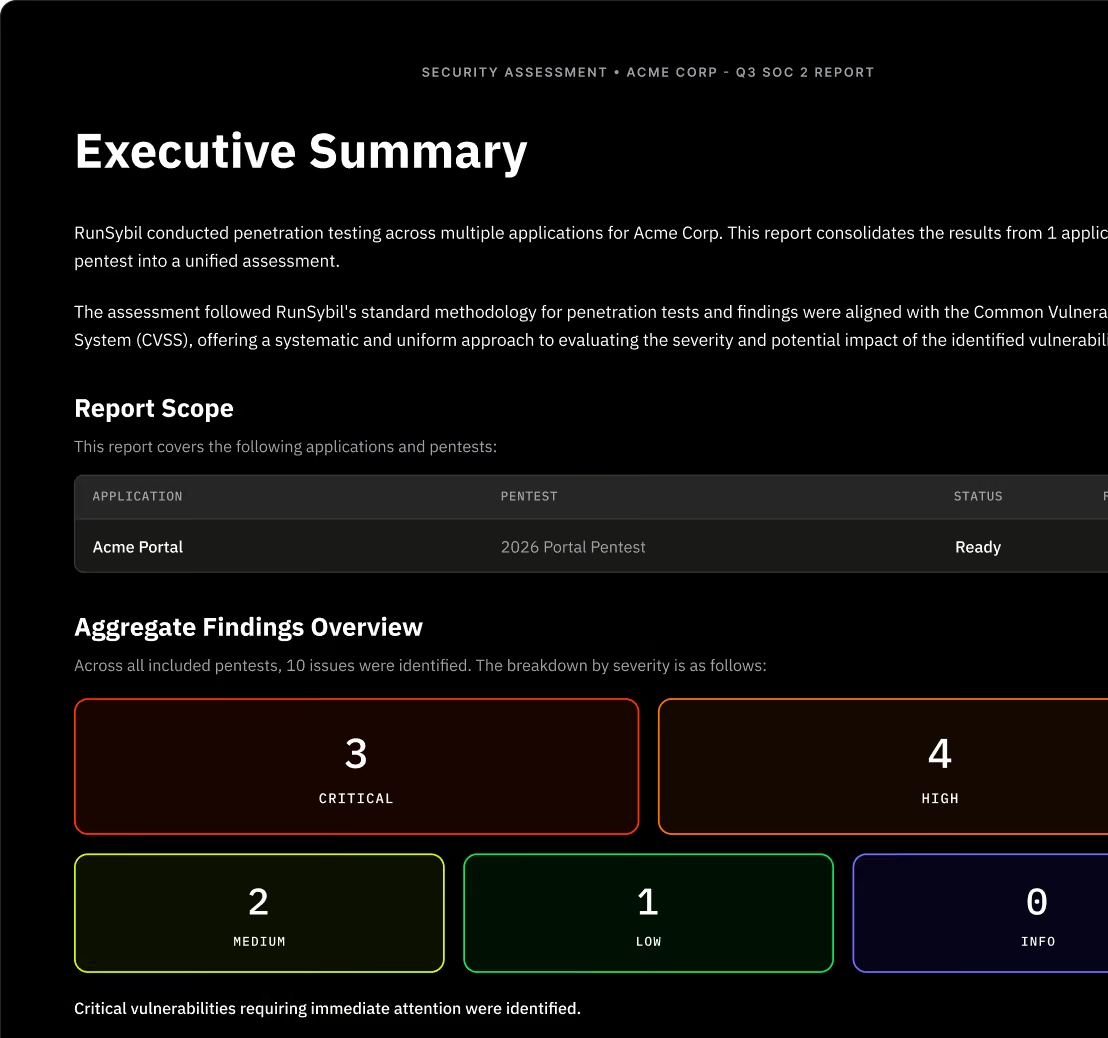
RunSybil is backed by $40M from Khosla Ventures.You'll know exactly what evidence your auditor expects, and how to get it before your audit window closes.


In practice, auditors expect one anyway. A validated pentest is the clearest evidence available for two specific criteria: CC4.1, monitoring activities, and CC7.1, identifying and responding to vulnerabilities. Most organizations pursuing a Type II report run at least one penetration test somewhere inside the audit period.
Skipping the test doesn't fail a SOC 2 audit outright. It shifts the burden elsewhere. Every adjacent control comes under closer scrutiny, and the gaps a pentest would have closed are harder to explain when your auditor asks for evidence you don't have.

"We like to feel confident that each new feature we're releasing is not going to be a security hazard."
Every finding runs through Sybil's multi-agent validation pipeline before it reaches your report. Nothing ships until it's confirmed exploitable, so your team isn't triaging noise on top of an audit deadline. Testing typically surfaces a first finding around 16 minutes after kickoff: evidence starts accumulating almost immediately, not after a multi-week ramp-up.
CC7.1 covers responding to vulnerabilities, not just finding them. Each finding carries a status, open, remediated, or retest-verified fixed, so your auditor sees a closed loop: what was found, what got fixed, and how the fix was confirmed, all in the same report.
Cursor turned to Sybil to keep pace with the security reviews and compliance evidence their enterprise deals required as they scaled. The engagement ran end-to-end within two weeks of first contact, and the report was immediately usable in security questionnaires and procurement. Retests run self-serve, no scheduling call required.
"Sybil has been great. Super helpful. Quick. Only positive things."


"RunSybil was an excellent partner for us. They pressure-tested our systems ahead of a major release and delivered fast, high-quality results at a competitive price on par with top pen-testing firms."

Frequently Asked Questions
SOC 2 doesn't explicitly require an external penetration test as part of its Trust Services Criteria. In practice, auditors consistently expect one as evidence under Monitoring Activities (CC4.1) and vulnerability identification (CC7.1), particularly for a Type II report. The AICPA's criteria are outcome-based rather than prescriptive, so organizations choose their own methods to demonstrate controls are working, but a validated pentest is one of the clearest, most commonly accepted ways to do that. Skipping one doesn't automatically fail an audit, but it typically puts other controls under closer scrutiny.
Yes. Sybil's penetration testing reports are built to satisfy SOC 2 requirements asked for by auditors without reformatting. Each includes CVSS 3.1 severity scoring, CWE identifiers, a documented and validated exploit chain, remediation status per finding, and an executive summary mapped to the relevant Trust Services Criteria. This differs from raw scanner output, which most auditors reject since it lacks confirmation that a flagged issue is genuinely exploitable, let alone that it was fixed. Because Sybil validates findings before reporting and tracks each one through to a retest-verified fix, the evidence reflects confirmed, exploitable risk and a documented response, not just a list of what was found.
Testing can typically begin the same day an engagement is scoped, with no lengthy onboarding required, and retests confirming a fix can complete in under an hour rather than a new scheduled engagement. This matters for compliance timelines, where a finding identified close to a deadline still needs remediation and re-verification before the evidence package is submitted. Traditional pentest engagements can take weeks to months between scoping, testing, and retesting, which can leave little runway if testing starts late in the observation window.
A Type I audit evaluates whether controls are suitably designed at a single point in time. A Type II audit evaluates whether those same controls operated effectively over an extended period, usually 3 to 12 months. For pentesting, a Type I audit can generally be supported by one test close to the audit date. For a Type II audit, auditors consider when testing ran within the observation window, so most organizations schedule it early enough to remediate and retest before the window closes.